Resource: Blog

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Tier 1 bank should ask any decisioning vendor

Build or Buy Is the Wrong Question. Own What Your Decisions Learn.

Seven questions a Tier 1 bank should ask any decisioning vendor

When a bank asks me whether it should build or buy its decisioning platform, I usually answer with a different question: What do you need to own to compete, and what should you never build yourself?

Answering starts with recognizing that decisioning isn’t one capability anymore. It’s three.

The platform is the governed environment that orchestrates data, models, and increasingly AI agents, executes decisions in real time, and connects to whatever core systems you run. The differentiation is your credit policy, your risk appetite, your data, and the models trained on it: the judgment that makes the bank yours. The learning loop is how outcomes feed back to sharpen those decisions over time: changes simulated before they go live, performance monitored after, and evidence of what worked. These are different problems, and they have different answers.

McKinsey has argued that banks can take next-generation credit models from concept to deployment in under six months, compared with the 12 to 24 months that had been typical, by building on their own data and business expertise. For a bank with €50 billion in assets, it put the prize at €100–200 million in additional annual profit. Look at where that value sits: in the models and the judgment behind them, not in the engine. I’ve rarely seen a bank win on the engine, and I’ve seen several quietly write off an in-house build that took three years to almost work.

So, the skill isn’t choosing to build or buy, but drawing the line in the right place. Own the judgment: your policy, your risk appetite, your data, and the models trained on it, including the right to take them with you. Buy the platform. Let it run the learning loop but make sure you own what the loop learns. And where you buy expertise, buy it in a form that builds your team’s own capability.

Then press hard on whoever sits on the buy side of that line. These are the questions I’d put to any decisioning vendor. I run applied intelligence at a decisioning platform company, so read them knowing my bias, and knowing I’ve kept in the ones that are hardest for firms like mine to answer. Ask them of my company too. Many of them also appear in IDC’s advice to technology buyers in its 2026 assessment of decision intelligence platforms (Provenir was among the vendors evaluated).

1. How fast can we change a decision without you?

If the honest answer is a statement of work and a six-week queue for professional services, you haven’t bought a platform, you’ve rented a dependency. The reason to buy is to move faster than you could alone, so test it in the room. Ask them to change a live policy rule while you watch.

2. Where does our decision logic live, and can we take it with us?

This is the question vendors least like being asked, which is exactly why you should ask it.

Find out where your rules, models, decision history, and the lessons learned from your outcomes actually live, and in what form they leave the building if you walk. Ask where it all runs, too: which cloud or data center, which jurisdiction, and what happens to your decisions on the vendor’s worst day. For EU banks, this isn’t optional. Under the Digital Operational Resilience Act, you already need a documented exit strategy for any ICT provider supporting a critical or important function. A vendor confident in its value doesn’t flinch at the exit question.

3. Can you make our decisions defensible to a regulator?

Ask whether logging, versioning, explainability, and human override are built into the platform, or bolted on the day an examiner asks why a customer was declined. Ask whether your model risk team can validate every model in the flow, including the ones the vendor supplied. The pressure is coming from every direction.

Under the EU AI Act, credit scoring is a high-risk use; the Digital Omnibus pushed the deadline to December 2027 but didn’t remove it, and the Fundamental Rights Impact Assessment sits with you, the deployer, even when the model came from a vendor. In the US, adverse action rules already require specific reasons for every decline, whatever model produced it. Governance you can’t reconstruct isn’t governance.

4. When you say agentic AI, show me.

Nearly every vendor deck in 2026 has an agent on it. IDC found that most vendors expect agentic AI to be used for authoring, updating, or explaining decision logic, not for making the decision itself, and that regulated use cases keep the final decision deterministic. That’s the right instinct for a bank. Don’t ask whether the AI is autonomous. Ask whether every automated decision can be traced to the data, rule, and model version that produced it, then replayed, explained, and overridden. If it can’t, it doesn’t belong anywhere near your book.

5. How fast can we put a new data source or a new model to work?

Your advantage over the next five years will come from signals and models that aren’t in your stack today: cash-flow data, new bureau attributes, a sharper fraud model, whichever large language model you trust next year.

So, ask two things. How long does a new data integration take: weeks, or months? And can you bring any model into the decision flow, whether your own data scientists built it, a third party did, or it comes from a provider you haven’t chosen yet, under the same governance and without re-platforming? A platform that only works well with its own models and its own data partners is a ceiling, not a foundation.

6. Will we be more capable in year three, or more dependent?

A platform makes you more capable of doing your own work. A project makes you dependent on someone else doing it for you. You’re almost certainly not starting from scratch, so start with the path: ask how you move off what you run today, use case by use case, without a big-bang cutover. Then ask the vendor to name what your team will be able to do alone in year three that it can’t do today. A good partner can answer both.

7. How will you prove it worked, and what will it cost us to find out?

Agree on the baseline and the KPIs before you sign, not after go-live: approval rates, loss rates, decision speed, and how quickly you can make changes. Ask to see a proposed change simulated against your own historical data before it goes live, with the shift in approval, referral, and decline rates in front of you. Then model the total cost as your volumes grow, not just the year-one license. A vendor that wants to be measured will help you set the bar. One that doesn’t will want to talk about features.

Gartner published its first Magic Quadrant for Decision Intelligence Platforms in January, and IDC followed with its MarketScape in September. When a category draws that kind of attention, the market is telling you this is infrastructure you buy and build on. But an analyst assessment tells you who the serious vendors are, not where your own line should sit. IDC’s lead analyst put the remaining question well: leaders need to consider “how much control the organization retains over decisions that carry regulatory or operational significance.” No analyst and no vendor can answer that for you.

So, here’s where I land. Stop treating build versus buy as a single switch. Decide deliberately which part of the decision layer you must own: your policy, your models, your data, what your decisions learn, and your exit. Then buy the platform that makes owning those things faster and more defensible and hold it to the seven questions above. Buy leverage, not dependency.

The banks that win the next decade won’t be the ones that built the most, or the ones that outsourced the most. They’ll be the ones that were clearest about the difference.

If you’re drawing that line right now, I’m happy to compare notes.
Eric

Eric Stonier

Written By

Executive Vice President Global Applied Intelligence, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Decisioning Platform Can’t Answer (But Should)

5 Questions Your Decisioning Platform Can’t Answer(But Should)

Most decisioning platforms can tell you what happened. Fewer can tell you why, and fewer still can tell you what to do next. That distinction rarely shows up in a demo. It shows up six months later, when a regulator asks for an explanation, a policy change produces an unexpected result, or a risk team spends a week reconstructing a decision that should have taken a search bar and thirty seconds.

The five questions below come up constantly in conversations with risk and fraud teams evaluating their current setup. They are simple to ask and, for a lot of platforms, surprisingly hard to answer. If your platform can’t answer them, that’s worth a closer look, not because the platform is broken, but because it may have been built to execute decisions rather than to give you visibility and control over them.

1. Why was this specific decision made?

Not the rule that fired. The full picture: which data, which model, which policy version, and which override, if any, produced this exact outcome for this exact customer. If the honest answer takes a support ticket and two days to reconstruct, that’s not an explainability problem you can solve after the fact. It’s a governance gap baked into the architecture.

Picture an audit request for a decision made eight months ago. The team that fielded it needs to pull the policy version live at the time, the data inputs available in that moment, and any manual override applied along the way, often from three different systems that were never designed to be queried together. That reconstruction effort is the tell. A platform built for governance answers the question at the moment it’s asked, not after a week of forensic work.

2. What would happen if we changed this policy, before we change it?

Most teams find out what a policy change does by shipping it and watching the numbers move. That’s a live experiment run on real customers and real risk exposure. A platform built for control lets you simulate a strategy change against production data first, so the decision to deploy is based on evidence rather than confidence.

Tightening a fraud threshold is a good example. Do it live, and you find out in real time whether you also blocked a wave of legitimate customers, usually after the complaints start coming in. Simulate it first against actual production traffic, and you know the approval and fraud-catch tradeoff before a single real customer is affected by the change.

3. How consistent is this decision across every channel and product?

If credit, fraud, and collections run on separate systems, the honest answer is often “we’re not sure.” A policy tightened in one system doesn’t automatically show up in the others, which means the same customer can get inconsistent treatment depending on which system happened to touch their file. Consistency across the lifecycle isn’t a reporting exercise. It’s a structural property of whether decisioning runs on one governed environment or several disconnected ones.

4. How is this model performing right now, not last quarter?

Model monitoring on a monthly or quarterly cadence means degraded performance can run for weeks before anyone notices. Continuous monitoring closes that gap, and it also closes a harder one: knowing not just that performance dropped, but what changed and what to do about it, in time to act rather than explain after the fact.

5. Can the business make this change, or does it need to wait on IT?

This is often the real bottleneck. A risk team identifies a needed change, and then waits weeks or months for engineering capacity to implement it. If every strategy adjustment requires a development cycle, decisioning speed is capped by IT throughput, not by risk appetite or market opportunity. A platform that lets business teams configure and deploy strategy changes directly removes that ceiling, without removing the governance that has to stay in place.

A risk team that spots a fast-moving fraud pattern on a Monday and can’t get the fix into production until an IT sprint clears in three weeks isn’t a risk-appetite problem. It’s a build queue problem wearing a risk-appetite costume. The gap between when a team knows what needs to change and when that change actually reaches customers is usually the clearest sign of where control actually sits.

Where does your team stand?

If your organization can answer all five of these without a delay, a workaround, or a shrug, your decisioning platform is likely already doing its job. If not, the gap is usually architectural rather than a training issue: it’s what happens when decisioning logic is spread across systems that were never designed to be one thing.

Andrew

Andrew Beddoes

Written By

Principal Consultant PreSales & Solutions, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Include in Your Decision Management RFP

10 Questions to Include in Your Decision Management RFP

If your institution is considering replacing its decision management platform, the RFP is where that process starts. The platform you choose will run your credit, fraud, and customer decisions for years, so the questions you ask up front matter.

Below are 10 questions we recommend every bank and financial institution include in their RFP, along with how Provenir answers each one.

1. Can a single platform support decisioning across the full customer lifecycle?

Yes. Provenir supports origination, account management, collections, and fraud on one platform, with shared data integrations, models, attributes, and governance.

Institutions can implement each use case as its own service while reusing common components, which removes duplicate logic and inconsistent treatment across products and channels. Customers avoid stitching together separate engines for each stage of the lifecycle.

2. Are we locked into a single data provider?

No. Provenir is vendor-neutral by design. The Provenir Data Marketplace provides pre-built, fully managed integrations to more than 150 global and local data providers, covering credit bureaus, fraud, identity, KYC/KYB, open banking, and alternative data.

Institutions can use their existing provider contracts and credentials. New sources are onboarded through a no-code connector framework rather than custom development, so your data strategy is never dictated by your decisioning vendor.

3. Can business users change strategies without depending on IT?

Yes, Business users have the full ability to manger their strategies, within a governed framework. Authorized risk and strategy teams can build, test, and deploy rules, decision trees, scorecards, and champion/challenger strategies through a low-code studio. Every change is controlled by:

  • Version control with check-in/check-out, user attribution, and rollback
  • Controlled promotion across Development, QA, and Production, with no direct production edits
  • Segregation of duties enforced through role-based access

The result is business agility without compromising audit or regulatory control.

4. How do you prove the impact of a policy change before it goes live?

Provenir’s native Simulation replays historical production decisions through proposed strategies using the original inputs and stored third-party responses. Teams can measure the impact on approval rates, risk distribution, and segment performance without re-calling data providers or incurring additional data costs.

Combined with champion/challenger testing in both real-time and batch, institutions can reduce strategy testing cycles from months to weeks.

5. Can the platform handle real-time and high-volume batch decisioning at the same time?

Yes. Provenir runs real-time and batch workloads on separate, independently scaled engines, so a large overnight portfolio run never affects latency-sensitive origination traffic. In production, the platform supports more than 10,000 real-time transactions per second and more than 50 million batch records per hour.

6. Can we deploy our own models, and how are they governed?

Yes. Provenir supports bring-your-own-model deployment for Python, R, PMML, Java, and Excel-based models. Models execute natively within the decision flow and are versioned alongside the data attributes that feed them.

Built-in model monitoring, drift detection, and champion/challenger testing support model risk management. Institutions without dedicated data science teams can also build and retrain models in-platform with Provenir AI.

7. How does the platform support explainability and regulatory compliance?

Every execution produces a complete decision trace capturing inputs, data sources, rules, model outputs, reason codes, and final outcomes. Provenir supports SHAP- and LIME-based local and global explainability and automated adverse action and reason code generation, mapped to the institution’s own taxonomy.

Combined with full change-management logging, this gives institutions audit-ready evidence for regulators, model validators, and fair lending reviews.

8. How is the platform using AI, and how is that AI governed?

Provenir embeds AI with human-in-the-loop controls by design. The platform’s AI assistant lets users query data, interpret decision logic, and automate tasks in natural language.

Provider-agnostic LLM integration (including OpenAI, Anthropic, and privately hosted models via AWS Bedrock) lets institutions choose the right model for each workload without re-platforming. Every AI-assisted decision remains transparent, explainable, and subject to the same governance as any other strategy change.

9. What is your architecture, availability, and security posture?

Provenir is a cloud-native platform built on AWS, fully containerized on Kubernetes (Amazon EKS), with multi-availability-zone deployment, self-healing infrastructure, and zero-downtime upgrades. Key commitments include:

  • Availability SLAs of up to 99.99%
  • SOC 2 Type II and ISO 27001 certification
  • AES-256 encryption at rest with AWS KMS, and TLS/mTLS in transit
  • SSO, MFA, and role-based access integrated with enterprise identity providers

10. How long does implementation take, and how do you reduce migration risk?

Provenir’s average implementation timeline is 6 to 12 months. For example, a top-15 U.S. credit card issuer went live on onboarding, account management, and pre-delinquency decisioning in nine months.

Migration risk is managed through parallel testing against the incumbent system, historical replay to prove decision parity, and version-controlled rollback. Institutions can then cut over with confidence rather than relying on a big-bang switch.

Choosing the right partner

Replacing a decision engine is a big decision, and the right platform should hold up to detailed scrutiny. Use these questions with every vendor in your evaluation, and ask each one to show you the answers live, not just describe them. The differences become clear quickly. If your team is starting to scope a replacement, we’re happy to walk through how Provenir handles each of these in a tailored demo, or act as a sounding board on your requirements.

sam

Sam Rhode

Written By
VP, PreSales & Solutions, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed: What Risk Leaders Are Actually Missing

Confidence at Speed:
What Risk Leaders Are Actually Missing

Most risk organizations are facing a similar problem: they need to move faster. More decisions, more channels, more pressure to approve in seconds rather than days. So the instinct is to buy for speed. Faster engines, faster models, faster onboarding. 

However, speed is not the problem most of these organizations actually have.  

Visibility is. 

At Provenir, we’ve had risk leaders who can tell us exactly how fast their systems approve an application but aren’t clear on why a given decision was made, whether it would hold up under regulatory review, or how a policy change three systems ago is still affecting today’s approval rate. That is not a speed gap. That is a control gap, and it’s the one that gets expensive. 

How the Gap Forms

It rarely happens on purpose. A credit engine gets bought to solve credit. A separate fraud tool gets added when fraud becomes the priority. Collections gets its own system when recovery rates slip. Each decision made sense in isolation. None of them were made with the others in the room.

Years later, the risk organization is running on a stack of tools that were never designed to share a data model, a decision log, or a governance framework. Authority over decisioning becomes diffuse: spread across systems, vendors, and teams, with no single place to see the whole picture. Strategy gets constrained by what the architecture can support, instead of the architecture supporting the strategy the business actually wants to run.

This is what flying blind looks like in practice. Not a lack of data. Too much data, scattered across systems that do not talk to each other, with no consolidated view of how a decision was actually made.

Picture a single customer moving through that environment. Credit approves them based on the data available at onboarding. Weeks later, the fraud system flags unusual activity on the account, working from a different data set and a different scoring logic, with no visibility into the credit decision that already happened. By the time the account reaches collections, the treatment strategy is built without either of those earlier signals. Three systems, three partial views, and no single place where a risk leader can see the full picture of that one relationship. Multiply that by a portfolio of millions of customers, and the visibility gap stops being an inconvenience. It becomes the reason risk teams get surprised by numbers that a connected system would have surfaced months earlier.

Why This Is The Moment It Matters Most

Three forces are converging on risk organizations right now, and each one raises the cost of staying fragmented.

AI adoption is outpacing AI governance. Risk teams are under pressure to bring AI and machine learning into decisioning faster than ever, but a model added to one system in isolation is a model nobody can fully explain across the customer’s full journey. The more AI gets layered onto a fragmented stack, the harder it becomes to answer a simple question: what, exactly, made this decision, and can we defend it.

Regulators are asking harder questions. Explainability and auditability are no longer boxes to check once a year. Examiners want to see, on demand, why a specific decision was made for a specific customer, and fragmented systems make that request expensive to fulfill even when the answer is defensible. The cost is not just the audit itself. It is the time risk teams spend reconstructing decisions after the fact instead of having the answer ready.

Vendor sprawl has stopped paying for itself. Every additional point solution came with its own contract, its own integration cost, and its own maintenance burden. Individually, each one looked justified. Collectively, they have become expensive to run and slow to change, and that cost shows up twice: once on the budget, and again in how long it takes to respond when the business needs to move.

Risk organizations that consolidate onto a single, governed decisioning environment are the ones positioned to manage risk deliberately rather than reactively. That is a different posture than moving fast. It is moving with your eyes open.

What Visibility Actually Buys You

A governed decisioning environment does not trade control for speed. It gets you both, in the right order.

When every decision is traceable and explainable by design, risk teams can calibrate exposure on purpose instead of discovering problems in a post-mortem. When strategy changes can be simulated and tested against real production data before they go live, business teams can move quickly because they have already validated the outcome, not because they are hoping for the best. When the full customer lifecycle runs through one system instead of four, a policy change made in one place shows up consistently everywhere it should, and nowhere it shouldn’t.

This is the shift I would ask every risk leader to consider: the goal was never speed for its own sake. It was confidence at speed. Those only coexist when the organization can see, end to end, exactly how and why every decision gets made.

Where This Leaves Risk Leaders

The organizations that will separate from the pack over the next few years are not the ones with the fastest single decision engine. They are the ones that closed the visibility gap first, and can move fast because they have full control over the decision layer, not in spite of it.

Brendan Deakin, Executive Vice President - Provenir

Brendan Deakin

Written By
Executive Vice President, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

BLOG Bharati Fernando

How to Change a Decisioning Model Without Raising a Ticket

How to Change a Decisioning Model Without Raising a Ticket

Reframing the Question

“Change a decisioning model without raising a ticket” reads at first as a request to bypass governance. A more productive reading treats it as a question of design: why does the ticket exist, and must the controls it represents continue to be administered through a change-management process that sits outside the decisioning environment?

In enterprise decisioning, governance serves a defined set of objectives. Changes must be attributable to an identifiable author, reviewable before they take effect, and testable against expected outcomes. Organisations must control who may make them, understand their downstream impact, and preserve a path to intervene when behaviour diverges from intent. These requirements are most acute where decisioning determines credit eligibility, pricing, fraud intervention and customer treatment, and where a poorly governed change can affect large populations before it is noticed. Traditionally, those objectives have been pursued through volume: sequential sign-offs and a uniform review applied to every change regardless of its risk. Yet rigour derives from what is actually examined, not from how many people approve it. An optimised model keeps the same requirements, namely documentation, testing, traceability and accountability, but applies them in risk-based tiers, so that the safeguards remain while the friction falls and speed ceases to be traded against safety. The ticket, on this view, is only an administrative instrument, separate from the control objectives it was introduced to satisfy.

Why This Matters More as Decision Intelligence Matures

That distinction grows more consequential as decision intelligence matures. The 2024 Gartner CDAO Agenda Survey found that a third of organisations have implemented decision intelligence, the practice of combining data, analytics and AI into decision flows that support or automate complex judgements. Gartner has since predicted that by 2027, half of business decisions will be augmented or automated by AI agents for decision intelligence. As greater intelligence enters the decision itself, the mechanisms governing changes to decisioning logic deserve comparable scrutiny.

Moving Control Inside the Platform

Provenir illustrates how much of that control can reside inside the decisioning environment rather than around it. Business teams configure, test and deploy decision logic directly, while the workflow remains auditable and version-controlled. Champion/challenger capabilities allow competing strategies to be evaluated, including against live data, before broader release. Configurable rules determine when a change must halt for manual review. Each capability reconstitutes something the ticket was there to guarantee: a record of what changed, a means of comparing outcomes, and a defined point at which human judgement is required.

From Operational Fix to Strategic Advantage

Framed strategically, removing the ticket is less an operational tidy-up than a shift in business model and in where competitive advantage sits. A decisioning model is rarely a durable advantage in itself, since techniques are published and comparable capabilities can be bought; what resists imitation is the organisational capacity to change decisioning logic rapidly and safely at scale, a dynamic capability through which a firm continually reconfigures its decision rules as conditions shift. Because that capacity emerges from many interacting elements, among them platform configuration, version-control discipline, champion/challenger routines and calibrated permissions, rivals cannot easily identify what produces the superior rate of safe change. That causal ambiguity is itself a barrier to imitation, and it turns a faster, safer change process from a passing operational gain into a defensible position: the decisioning function moves from issuing individual decisions to compounding many governed, evidence-tested changes into a lead that later entrants struggle to catch.

Oversight Is Shifting Too

This reframes oversight itself. Interpretability and explainability have increasingly shifted governance from after-the-fact audit toward continuous, built-in accountability. Where oversight once rested on testing outcomes and trusting that a model worked, it now tends to require evidence of why it works: documented feature importance, decision logic and traceable reasoning behind each score or flag. Governance frameworks increasingly expect explainability artefacts alongside performance metrics, among them model cards, decision logs and plain-language justifications that legal, compliance and audit functions can read, not only statisticians. That widens the table, drawing risk, compliance and legal teams into model changes earlier because they can understand what is being altered, and it makes each update something the organisation can defend rather than merely deploy. The economics point the same way: McKinsey’s March 2025 State of AI survey found CEO oversight of AI governance among the factors most correlated with higher self-reported bottom-line impact from generative AI, positioning governance less as a constraint on value than as a condition of it.

Where Governance Belongs

For decisioning, the implication is that governance belongs in the design and operation of the platform itself, with auditability, version control, testing, permissions, monitoring and defined points of human intervention embedded within the decisioning lifecycle rather than administered beside it. Removing a ticket is legitimate only once the control it represented has demonstrably been accounted for elsewhere. Where that condition is met, the firm has not simply deleted a step; it has relocated a source of advantage into a capability that rivals find difficult to observe, and harder still to replicate.

The maturity of a decisioning capability should therefore be assessed on more than the speed and accuracy of individual decisions. An equally telling measure is whether decisioning logic can be modified efficiently while the standards that govern those modifications hold, and whether that combination is distinctive enough to constitute strategic advantage rather than mere operational convenience.

Bharati Mohan

Bharati Mohan

Written By
Vice President, Global Applied Intelligence, Provenir

Fernando

Fernando Moreno Fernandez

Written By

Vice President, Global Applied Intelligence, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

Verifying the Invisible Subscriber

Verifying the Invisible Subscriber

Verifying the Invisible Subscriber

How Accessing 1datapipe on the Provenir Marketplace Can Unlock Device Financing and Microlending in Emerging Markets

Telcos across emerging markets are hitting a ceiling with their traditional business. Voice and SMS revenue keeps eroding and mobile data plans have become a commodity that gets re-priced downward whenever a new entrant undercuts on tariffs. Average Revenue Per User (ARPU) is flat or falling in market after market.

Ultimately, as a telco operator, there are two ways to grow revenue: – add more subscribers or generate more revenue from your existing subscriber base.

In emerging markets, the greater challenge is attracting and onboarding new subscribers, most of whom have no credit bureau record. This article explores how telcos can reliably identify and onboard applicants quickly and cost-effectively without unknowingly admitting fraudsters or adding unnecessary delays and inconvenience to genuine customers.

Verifying the Subscriber when Traditional Credit History Doesn’t Exist

Every device-financing or microlending program in an emerging market runs into the same wall: how do you verify the individual or assess the onboarding risk when oftentimes there’s no mortgage history, revolving credit line, or credit bureau record. Traditional underwriting assumes a paper trail that a huge share of the addressable market in emerging markets simply doesn’t have.

The instinct is to reach for alternative data. The problem is that microloans and device financing — often $30 to $300 — cannot absorb a heavy per-applicant onboarding bill. A $2 all-in IDV call on a $50 handset loan isn’t a rounding error; it can be the entire margin. So, the real design question is where to use cost-effective alternative data, and where in the workflow it should sit.

How 1datapipe can Assist with Applicant Identity Verification

1datapipe is an identity intelligence partner recently added to the Provenir Data Marketplace, specializing in emerging markets. It builds on a deterministic identity graph across 30 emerging markets and describes its “Living Identity” approach as resolving fragmented data into persistent, verified identity entities maintained over time with full provenance, auditability and explainability, — as opposed to traditional providers who offer point-in-time verification as part of a broader, more expensive all-in IDV check typically including document authentication.

As well as asking “does this name, ID, and phone combination match the applicant’s submitted details right now?,” its ID Graph capability asks, “has this identity been stable and coherent over time, across multiple authoritative sources?” Coverage runs across markets in LATAM, Southeast Asia, MENA and Africa with over two billion verified profiles — precisely the geography where credit bureaus are patchy or absent.

Even if a credit bureau exists in a region, accessing a credit report presents a significant cost of acquisition; — often one that can wipe out much of the profit. Additionally, they can’t help with thin-file applicants, because there’s no credit history. So, the key questions are “is this person who they say they are, and have they existed consistently long enough to be a trustworthy counterparty?” Identity persistence becomes a proxy for stability when repayment history doesn’t exist.

Consequently, the more cost-effective approach treats identity verification as a waterfall. Placing deterministic identity resolution high in the waterfall, before credit bureau reports and/or extensive IDV checks, means you’re not paying for these checks — or an agent’s time — on an application that’s fraudulent, synthetic or duplicated.

1datapipe’s identity intelligence is a key factor in reducing fraudulent applications that erode the margins of telco and other microfinanciers, an issue growing in emerging markets where historically accurate and comprehensive identity data has been very challenging to access. Additionally, housing it within Provenir’s Data Marketplace allows lenders to leverage 1datapipe’s identity intelligence along with other data sources covering identity, fraud, credit risk, open banking and affordability without building and maintaining separate integrations. That “pick and mix” architecture is the difference between a six-month integration project per country and a configuration change in a decision flow.

Why this matters more for device financing and microloans than any other products

Larger loans can absorb a $5–$15 all-in verification cost because the ticket size and interest income justify it. Microloans and device financing can’t absorb that cost, which is exactly why they’re the products most often declined outright to avoid onboarding fraudulent applicants. In the process, however, genuine, thin-file applicants are declined, and the associated subscription revenue is lost. Accessing cost-effective data sources first and only accessing a credit report or IDV check for the applicants on which additional checks are warranted — is what turns “we can’t afford to know this customer” into “we can afford to serve this customer at a sustainable margin.” In markets where the credit data is thin, absent, or simply too expensive for a $75 handset loan, that sequencing decision is arguably more important than the underwriting model itself.

If these challenges resonate with you, learn more about 1datapipe® and how it enhances the Provenir ecosystem at the link below:

Learn More About 1datapipe®

Lucy King

Lucy King

Written By

Global Commercial director, 1DataPipe

mark-jackson

Mark Jackson

Written By
Director of Telco, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

FAQ

Decision Management Implementation FAQs for Enterprise Banks

Decision Management Implementation FAQs for Enterprise Banks

Implementing a new Decision Management platform is a significant undertaking for any enterprise bank, involving cross-functional teams, careful planning, and a shared commitment to getting it right. The following FAQs address the questions banks most often raise as they prepare for a Provenir implementation, from initial scope and governance to testing, go-live, and future expansion. Whether you’re evaluating what the process involves or preparing your team for a project already underway, these answers offer a practical look at what to expect at each stage.

1. What does implementing a new Decision Management platform actually involve?

A Decision Management implementation goes beyond configuring decision rules. A typical Provenir implementation can include defining the initial decisioning scope and workflows, integrating and orchestrating data, configuring case management and reporting, supporting model design and deployment, completing user acceptance testing, and preparing the solution for production go-live.

The exact scope is defined around the bank’s initial objectives, with Provenir Professional Services supporting the journey from initial implementation through future expansion.

2. Who from our bank needs to be involved in the implementation?

Enterprise implementations typically require participation from business, technical, quality assurance, project management, and executive stakeholders.

Business users help define and maintain requirements, participate in workshops and design reviews, execute business testing, and provide sign-off on design and go-live readiness. Technical teams support architecture, integrations, networking, security, encryption, request/response structures, and non-functional requirements. QA resources develop and execute test plans, while executive sponsors and steering committees provide governance and escalation oversight.

3. How much responsibility does our internal team have during implementation?

Implementation is a joint delivery effort rather than a vendor working independently and handing over a finished system.

The bank owns its business requirements, provides subject-matter expertise, participates in solution and design reviews, supports integrations and technical architecture, develops or executes relevant testing, and ultimately signs off on readiness. Provenir works alongside those teams to manage delivery, configure the solution, support testing, identify dependencies, manage issues, and prepare for production deployment.

4. How is a large Decision Management implementation governed?

Provenir uses a structured governance framework covering onboarding, resource planning, communications, escalation, scope control, assumptions, risk mitigation, change requests, timelines, deliverables, and advisory requirements.

Governance can include daily scrum calls where needed, weekly project-management meetings and status reporting, and monthly executive or steering-committee reviews. A central project plan, milestone tracking, action logs, risk and issue registers, and formal change-management processes provide visibility throughout delivery.

5. How do you keep scope, dependencies, and timelines under control?

Implementation planning starts by aligning on the finalized scope, requirements, assumptions, dependencies, critical milestones, design components, resources, testing cycles, communication plans, and escalation processes.

Provenir maintains these through project-management tools such as the integrated project plan, requirements and project checklists, milestone tracking, action-item management, risk and issue logs, and a formal change-request process. This gives both teams a common source of truth as the project progresses.

6. What documentation and planning should we expect before development begins?

A structured enterprise implementation typically includes a Business Requirements Document, Technical Design Document, high-level project plan, and a jointly agreed sprint breakdown.

Before build activities progress, the teams review the finalized scope, requirements, assumptions and dependencies, critical milestones, design components, resource availability, testing and validation cycles, planned holidays or blackout periods, and communication and escalation plans.

This upfront alignment helps ensure that business, technology, and delivery teams are working against the same requirements and implementation plan.

7. How is the solution tested before it goes into production?

Testing is performed progressively throughout the implementation rather than being left until the end.

The approach described by Provenir includes unit testing, integration testing, end-to-end workflow testing, QA and user acceptance testing, regression testing, and performance stress testing. Individual components are tested before being integrated into the overall decision workflow, and regression testing is performed throughout delivery to identify issues earlier and reduce the effort required during final validation.

8. How do we know the new Decision Management platform will meet our performance requirements?

Performance testing is included as a specific validation activity.

Provenir can use performance-testing tools such as JMeter to simulate large volumes of applications and measure system performance against the bank’s required service levels. This provides evidence that processing performance is meeting agreed expectations before the solution moves into production.

9. What happens once the initial implementation goes live?

Go-live is not the end of the relationship.

Provenir offers ongoing support subscriptions that can include training, configuration reviews, performance assessments, expert consultations, data and integration assessments, model and analytics reviews, and decision-strategy reviews. Training is also available through live sessions and Provenir Academy so internal teams can continue building their platform knowledge after implementation.

The objective is to support both stable day-to-day operation and continued optimization of the platform over time.

10. Can we expand into additional products, markets, or use cases after the first implementation?

Yes. Provenir’s implementation approach is designed to support expansion after the initial launch.

Follow-on projects can introduce additional products, regions, integrations, decisioning capabilities, or analytics requirements. Provenir can help define the scope and timeline of each expansion, prepare systems and teams for regional or product launches, and extend existing integration frameworks and platform configurations rather than treating each new initiative as an entirely separate implementation.

This allows the initial Decision Management deployment to become a foundation for broader decisioning transformation across the bank.

Sam Rohde

Sam Rohde

Written By
Vice President, PreSales & Solutions, Provenir

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Closing the Fraud Prevention Gap

Beyond Detection:
Closing the Fraud Prevention Gap

Financial services providers have more data, more models, and more fraud technology than at any point in the industry’s history. Fraud losses are still climbing. In 2024, consumers reported losing $12.5 billion to fraud, a 25% jump from the year before, according to the FTC’s Consumer Sentinel Network Data Book. Imposter scams alone accounted for over 847,000 reports.

It’s worth asking why more technology alone hasn’t closed the gap.

Fragmentation, not detection, is the real problem

Most fraud programs aren’t short on tools. They’re running point solutions for identity verification, device risk, watchlist screening, and behavioral analytics, each bolted onto the last, each with its own data feed and its own blind spots. Teams end up reacting to threats one system at a time instead of seeing the full picture in real time, while fraudsters move across channels and products, testing whatever gap opens first. A fragmented defense is always a step behind an adaptive attacker.

The biggest red flag: data that isn’t fit for purpose

The teams making real progress on fraud have a narrower data footprint, not a bigger one. What they have is matched precisely to the decisioning problem in front of them, and it plugs in without a six-month integration project.

The pattern shows up constantly: companies without a strong data foundation try to stitch one together after the fact, pulling in sources that weren’t built to work together and weren’t vetted for the decision at hand. The result creates the appearance of coverage while functioning as noise.

Fraud prevention runs on the same principle as any other decision: the data matters more than the volume of data collected. Access to the right source, at the right moment, beats access to more sources.

What a governed decision layer changes

Provenir’s Application Fraud solution brings identity signals, device intelligence, behavioral data, and watchlists into a single, governed decisioning environment instead of a stack of disconnected tools.

  • Behavioral and identity AI detects synthetic identity, first-party fraud, and emerging patterns through intelligent profiling instead of static rules alone.
  • Real-time threat blocking scores and stops threats as they happen, not after a batch review.
  • Smarter case management prioritizes queues so investigators spend time on the cases that matter, not chasing false positives.
  • A governed data marketplace gives fraud teams on-demand access to 120+ data partners across identity, device, and credit signals, with pre-built integrations instead of a new project every time a new source is needed.

The result is a single, governed view of risk that gets sharper with every decision it processes.

Proof in practice

MTN put this to work and stopped 135% more high-risk transactions, while increasing pre-approvals by 130%. Fraud control and growth moved together because the data and the decisioning were finally working from the same source of truth.

Own the decision layer

Fraud won’t stop evolving, and the providers who win will be the ones whose decisioning is governed, connected, and built to adapt as fast as the threats do.

Book a meeting to see Provenir’s fraud decisioning in action

Amy

Amy Sariego

Written By

Senior Content Manager, Provenir

Latest Resources

261023 - BLOG Eric - FeatureIMG - 62264
Blog, Banking, Decisioning /

Seven questions a Tier 1 bank should ...

Build or Buy Is the Wrong Question. Own What Your Decisions Learn ... Read More →
5 Questions Your Decisioning Platform Can't Answer (But Should)
Blog, Decisioning /

5 Questions Your Decisioning Platform...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most decisioning platforms can ... Read More →
261009 - BLOG Sam - FeatureIMG - 62069 (1)
Blog, Decisioning /

10 Questions to Include in Your Decis...

10 Questions to Include in Your Decision Management RFP If your institution ... Read More →
IDC
News, Decisioning, Provenir /

IDC MarketScape Names Provenir a Majo...

IDC MarketScape Names Provenir a Major Player PARSIPPANY, N.J., October 14, 2026 ... Read More →
Brendan Deakin, Executive Vice President at Provenir
Blog, Data /

Confidence at Speed: What Risk Leader...

Confidence at Speed:What Risk Leaders Are Actually Missing Most risk organizations are ... Read More →
IDC-Report
eBook, Decisioning, Provenir /

IDC Report 2026

Report Provenir has been positioned in the Major Players Category in the ... Read More →
BLOG Bharati Fernando
Blog, Decisioning /

How to Change a Decisioning Model Wit...

How to Change a Decisioning Model Without Raising a Ticket Reframing the ... Read More →
PR Chartis
News, Fraud /

Provenir Named a Category Leader by C...

Provenir Named a Category Leader by Chartis Research in Fraud and Credit ... Read More →
Telco EBook
eBook, Telco /

How to Grow a Thriving Telecom Busine...

Ebook How to Grow a Thriving Telecom Business in the Global Market ... Read More →
WEBINAR on-demand Fraud
Webinar, Fraud /

The New Face of First-Party Fraud

On-Demand Webinar The New Face of First-Party Fraud: Three Personas Every Lender ... Read More →
Verifying the Invisible Subscriber
Blog, Telco /

Verifying the Invisible Subscriber

Verifying the Invisible Subscriber How Accessing 1datapipe on the Provenir Marketplace Can ... Read More →
FAQ
Blog, Banking /

Decision Management Implementation FA...

Decision Management Implementation FAQs for Enterprise Banks Implementing a new Decision Management ... Read More →
Compliance and Decisioning in North America - Claire Hartley
Decisioning /

From Regulatory Complexity to Competi...

FFrom Regulatory Complexity to Competitive Confidence:How Provenir Supports Responsible Decisioning Across North ... Read More →
EBOOK Telco - FeatureIMG
eBook, Telco /

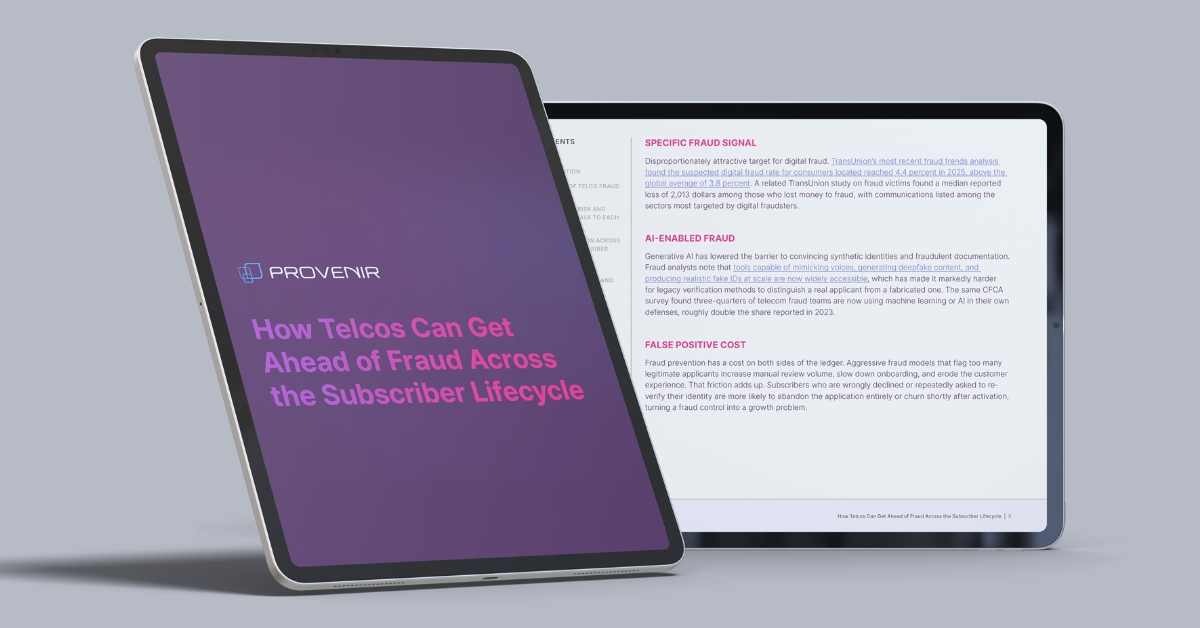
How Telcos Can Get Ahead of Fraud Acr...

Ebook How Telcos Can Get Ahead of Fraud Across the Subscriber Lifecycle ... Read More →
260814 - Data Parter Marginalen - social tile 1200x628 - GL_EN 61430
News, Decisioning /

Marginalen Bank Modernises Decisionin...

Marginalen Bank Modernises Decisioning Platform with Provenir's Cloud Native Decision Intelligence Platform ... Read More →

Continue reading

260726 - BLOG eyeDP - FeatureIMG - 61058

Beyond Data: Why Decisioning Needs Document Intelligence

Beyond Data:
Why Decisioning Needs Document Intelligence

Financial services providers now have access to more data than at any point in the industry’s history. Identity verification, fraud intelligence, credit data, sanctions screening, behavioral analytics and open banking have all become standard components of a modern decisioning strategy. Platforms like Provenir have made it possible to bring these sources together into a single, governed decisioning environment, replacing fragmented tools with consistent, auditable execution across the customer lifecycle.

One challenge has remained constant through all of this progress: many of the decisions that matter most still depend on documents.

Onboarding a new customer, verifying affordability, assessing source of funds, satisfying a regulatory obligation — each of these still relies on bank statements, payslips, proof of address, tax records, company filings and dozens of other forms of evidence. These documents carry essential information, and they remain one of the hardest sources of data to validate accurately at scale.

That gap points to a broader shift underway across the industry. Effective decisioning is no longer only a question of what data an institution can access. It is a question of how much confidence that institution can place in the evidence behind every decision.

Structured data provides insight. Documents provide evidence.

Modern decisioning platforms are built to aggregate structured information well. They retrieve identity records, calculate risk scores, assess affordability and combine multiple data providers into a single workflow, giving institutions the orchestration needed to automate complex decisions while keeping governance intact.

Documents present a different kind of problem. They vary in format, quality and completeness, and much of what they contain cannot simply be extracted into predefined fields. Determining whether a document is internally consistent, whether it aligns with other evidence the customer has provided, whether it shows signs of alteration, and whether external public records support what it claims all requires interpretation, not extraction. That interpretation is where document intelligence becomes necessary.

The missing layer in decisioning

Document intelligence is not a replacement for decision orchestration. It strengthens it, by improving the quality of the evidence entering the decision-making process in the first place. Rather than simply pulling data out of a document, AI-powered document processing analyzes its content, flags inconsistencies, detects signs of manipulation and validates the information against trusted external sources.

This shifts the work from document collection to document understanding, giving institutions a more complete view of customer identity and risk. The outcome is stronger fraud detection, tighter compliance and greater confidence in automated decisions, without adding friction for genuine customers.

Why complementary technologies matter

As institutions modernize their technology stacks, the strongest strategies are built on connected ecosystems rather than standalone tools. A governed decisioning environment provides the framework for bringing multiple sources of intelligence together into one consistent workflow. Specialist technologies then contribute depth in their own domain, whether that domain is identity verification, fraud prevention, credit intelligence or document analysis.

This is what allows institutions to adopt best-in-class capabilities in each area without giving up flexibility or control. Instead of asking a single technology to solve every problem, an institution can assemble an ecosystem in which each solution adds distinct value while reinforcing the overall decision.

Bringing document intelligence into the Provenir ecosystem

The addition of eyeDP to the Provenir Data Marketplace is a direct example of this approach in practice. Through the Marketplace, institutions can now access eyeDP’s document intelligence capabilities directly within their existing Provenir workflows, putting document verification alongside identity, fraud and credit data as another governed input into the decision.

eyeDP analyzes documents across common formats, including PDFs, JPEGs and screenshots. Beyond extraction, it identifies discrepancies, flags potential fraud and cross-references document content against trusted public data sources, giving institutions greater confidence in the evidence behind every customer decision.

For institutions operating in regulated environments, the practical impact is direct: faster and more consistent onboarding, earlier identification of fraud risk, stronger compliance processes and less manual document review, all without giving up oversight.

The evidence behind every decision

The next stage of digital decisioning will not be defined by a single technology. It will be shaped by connected ecosystems in which specialist capabilities work together to improve both efficiency and confidence.

Decision orchestration provides the structure. Data providers contribute insight. Document intelligence strengthens the evidence underneath the decision itself. Together, they move institutions beyond simply automating decisions and toward decisions they can stand behind.

As the demands placed on regulated businesses continue to grow, confidence will matter as much as speed. Combining governed decision orchestration with document intelligence gives institutions a stronger foundation for every decision that follows, and a clearer path to reducing fraud, strengthening compliance and delivering the kind of customer experience that regulated growth depends on.

eyeDP

eyeDP provides advanced AI-powered document intelligence to help organisations reduce fraud risk, improve data integrity, and accelerate onboarding.

Learn More

JessWhitehouse

Jess Whitehouse

Written By

Director of Customer Operations, eyeDP

Latest Blogs

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading

Fraud in Telco: Provenir Experts Answer Frequently Asked Questions

Fraud in Telco:
Provenir Experts Answer Frequently Asked Questions

1. Regarding the 1st party fraud problem, there are fraud losses in the bad debt P&L, usage is monitored by the FMS, applications are handled by Credit risk, and nobody generally owns first-party fraud. Concretely, what type of solution can fix an organizational problem? Software doesn’t change reporting lines…
it is right that software alone doesn’t fix org charts, but the silo persists because fraud and credit run on separate systems with separate data. When application fraud scoring, credit decisioning, and intent-to-pay signals run in one orchestrated decision flow, you can finally tag an account as first-party fraud risk at origination and pass that flag downstream into collections strategy. The output, in addition to delivering a decline/approve, can be a shared risk label both teams act on. Several of our clients started exactly there: a joint fraud-credit decision workflow, before touching any reporting line.
2. By the time we detect a fraud, the handset is often already shipped. What new signal do you suggest to use, and at what latency?
The honest answer is: probably no single signal you don’t have yet. The gap is combining them in real time at the decision point : device fingerprint change, behavioral velocity, network signals via CAMARA/Open Gateway APIs… most operators have access to these, but they sit in different tools and never converge before the order is approved. We believe orchestrating those calls in a waterfall within the transaction, milliseconds, not batch, is the right approach.
3. We see fraud-as-a-service kits iterating daily, but my rule team takes up to 3 weeks to deploy a change through IT or requires a change request to our vendor. Every vendor says “AI fights AI”, but can you concretely explain how to better manage time-to-deploy for a new model or rule, and who needs to be in charge?
Fair challenge, and it’s the right metric to buy on. In our platform the fraud team owns the decision logic: low-code, so a rule change or a champion/challenger test is deployed by your analysts in hours, outside usual IT release cycles. On the model side, you can drop in a retrained model alongside the live one, route 10% of traffic, and compare before switching. The point isn’t that our AI is smarter than theirs, but very design of the solution makes the iteration loop become shorter, which is the only durable advantage.
4. We get blamed for fraud losses as well as for abandoned carts. Can you share real numbers that back the frictionless security headline? Referral rate, false positive reduction… and how do you also measure the revenue side?
We’d never quote a universal number, because is primarily depends on the baseline referral rate. What matters is the mechanism. A risk-based waterfall, where low-risk applicants pass on cheap passive checks; data costs and friction are only escalated for the ambiguous middle. That alone typically collapses the manual review queue, because most referrals today are caused by blunt, one-size-fits-all rules. And because the decisioning and the data are in one place, we build the conversion dashboard next to the fraud dashboard. And our simulation capability makes it easy to assess instantly the impacts on both conversion and loss. That dual KPI view is, frankly, how fraud managers can better defend their budget.
5. We’ve got a 15-year-old FMS that’s excellent at IRSF, but useless at onboarding, plus a credit engine, plus a KYC vendor, plus device intelligence. You’re proposing to be tool number five. That’s yet another integration project in our IT backlog. All that for just orchestration. Realistically, when could we expect decisions in Production?
Your 5th tool objection would be legitimate if we were another point solution. Although we explained how powerful our proprietary Fraud block is, our platform sits as the decision layer that calls your existing four vendors through pre-built integrations from our data marketplace, so the business case is consolidating the decision, not replacing the tools. Typical first use case: say, online subscription with device financing. It goes live in weeks because there’s no rip-and-replace: your FMS keeps doing IRSF, we handle the onboarding decision it was never designed for. And over time you get leverage on those four contracts, because you can swap a data provider in the waterfall without touching the journey.
6. What innovations are you seeing across the eco system to combat this?

The biggest innovation is what could be called Open Telco: GSMA Open Gateway and CAMARA APIs turning network intelligence into usable fraud signals. APIs such as SIM Swap, Number Verification, Device Swap, KYC Match or Number Recycling help detect account takeover, fake onboarding, mule activity and social-engineering risks in real time.

But these signals are not a standalone answer. They become powerful when combined with device intelligence, behavioural analytics, graph analysis, AI-assisted investigation and dynamic step-up controls. The real innovation is orchestration: using better ecosystem signals to make faster, proportionate and explainable fraud decisions.

Have more questions?

Contact Us

LATEST BLOGS

261023 - BLOG Eric - FeatureIMG - 62264

Seven questions a Ti...

Build or Buy Is the Wrong Question. Own What
5 Questions Your Decisioning Platform Can't Answer (But Should)

5 Questions Your Dec...

5 Questions Your Decisioning Platform Can't Answer(But Should) Most
261009 - BLOG Sam - FeatureIMG - 62069 (1)

10 Questions to Incl...

10 Questions to Include in Your Decision Management RFP
Brendan Deakin, Executive Vice President at Provenir

Confidence at Speed:...

Confidence at Speed:What Risk Leaders Are Actually Missing Most
BLOG Bharati Fernando

How to Change a Deci...

How to Change a Decisioning Model Without Raising a
Verifying the Invisible Subscriber

Verifying the Invisi...

Verifying the Invisible Subscriber How Accessing 1datapipe on the
FAQ

Decision Management ...

Decision Management Implementation FAQs for Enterprise Banks Implementing a
260817 - BLOG Closing Fraud Gap - FeatureIMG - EN 61409

Beyond Detection: Cl...

Beyond Detection:Closing the Fraud Prevention Gap Financial services providers

Continue reading